About VicByte Advisory
One partner for security assurance, testing and capability.
VicByte Advisory is a Melbourne-based security advisory firm. We help organisations get certified, prove their defences work, and build the in-house skills to stay secure long after the engagement ends.
Our story
Built on discipline. Tested on mountains.
Deepak and Yusuf have been friends since 2007, but the foundation goes back further than that. Both grew up in Indian Army cantonments, sons of Army officers, in an environment where discipline, leadership and punctuality weren't lessons; they were simply how the day worked.
That foundation shaped two careers that ran alongside each other through Reliance Industries and Tata Steel, and two Master of Cybersecurity degrees from Monash University. It also shaped how they spend their time away from work: summiting peaks above 6,000m in the Himalayas, riding motorcycles from India to Bhutan, climbing Mt Bogong, Victoria's highest peak.
None of that is a hobby mentioned in passing. A mountain doesn't forgive a skipped check. A multi-day ride across borders doesn't forgive a plan with gaps in it. That is the same mindset VicByte brings to a security engagement: assess the real risk, prepare for what can go wrong, and execute without shortcuts. It's not a metaphor they reach for. It's the only way either of them has ever worked.
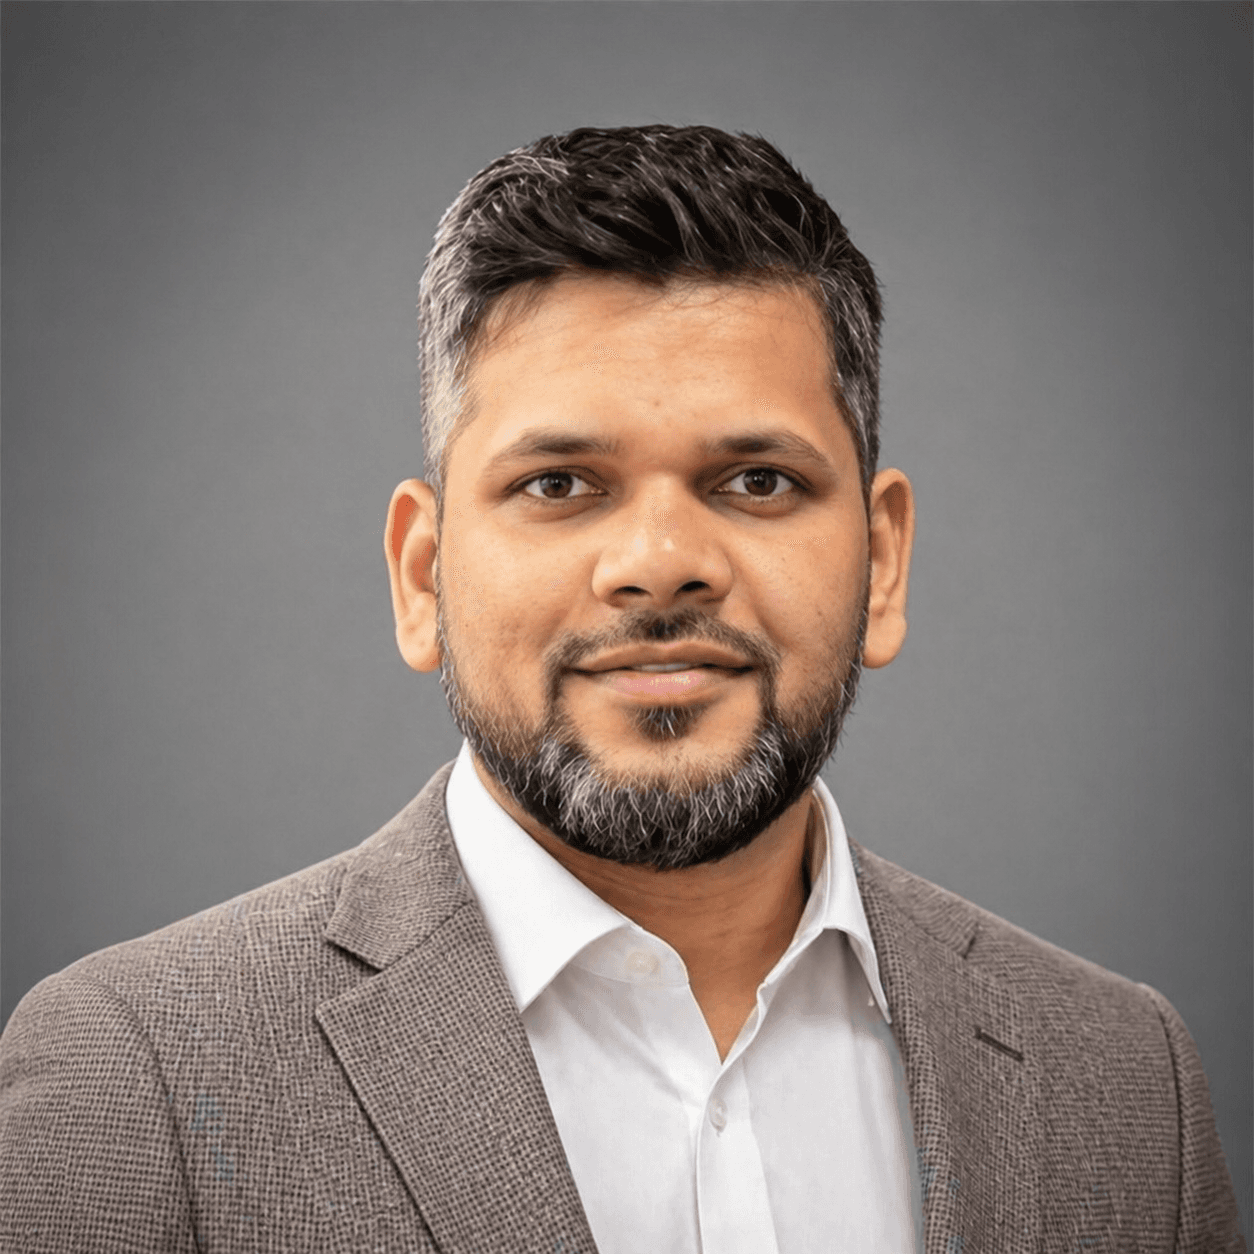
Director, Principal Consultant
Deepak Varma
Deepak is an ISO 27001 Lead Auditor, a CompTIA Security+ holder, and a Monash University Master of Cybersecurity graduate with over 11 years of hands-on experience spanning physical security governance and enterprise cybersecurity.
Before founding VicByte, Deepak led security and intelligence governance at Tata Steel, one of the world’s largest steel producers, designing governance frameworks, executing internal audits, managing risk registers, and reporting directly to senior leadership across multiple jurisdictions.
That practitioner background shapes everything VicByte delivers: advice from someone who has lived the consequences of a security gap, not just read the standard.
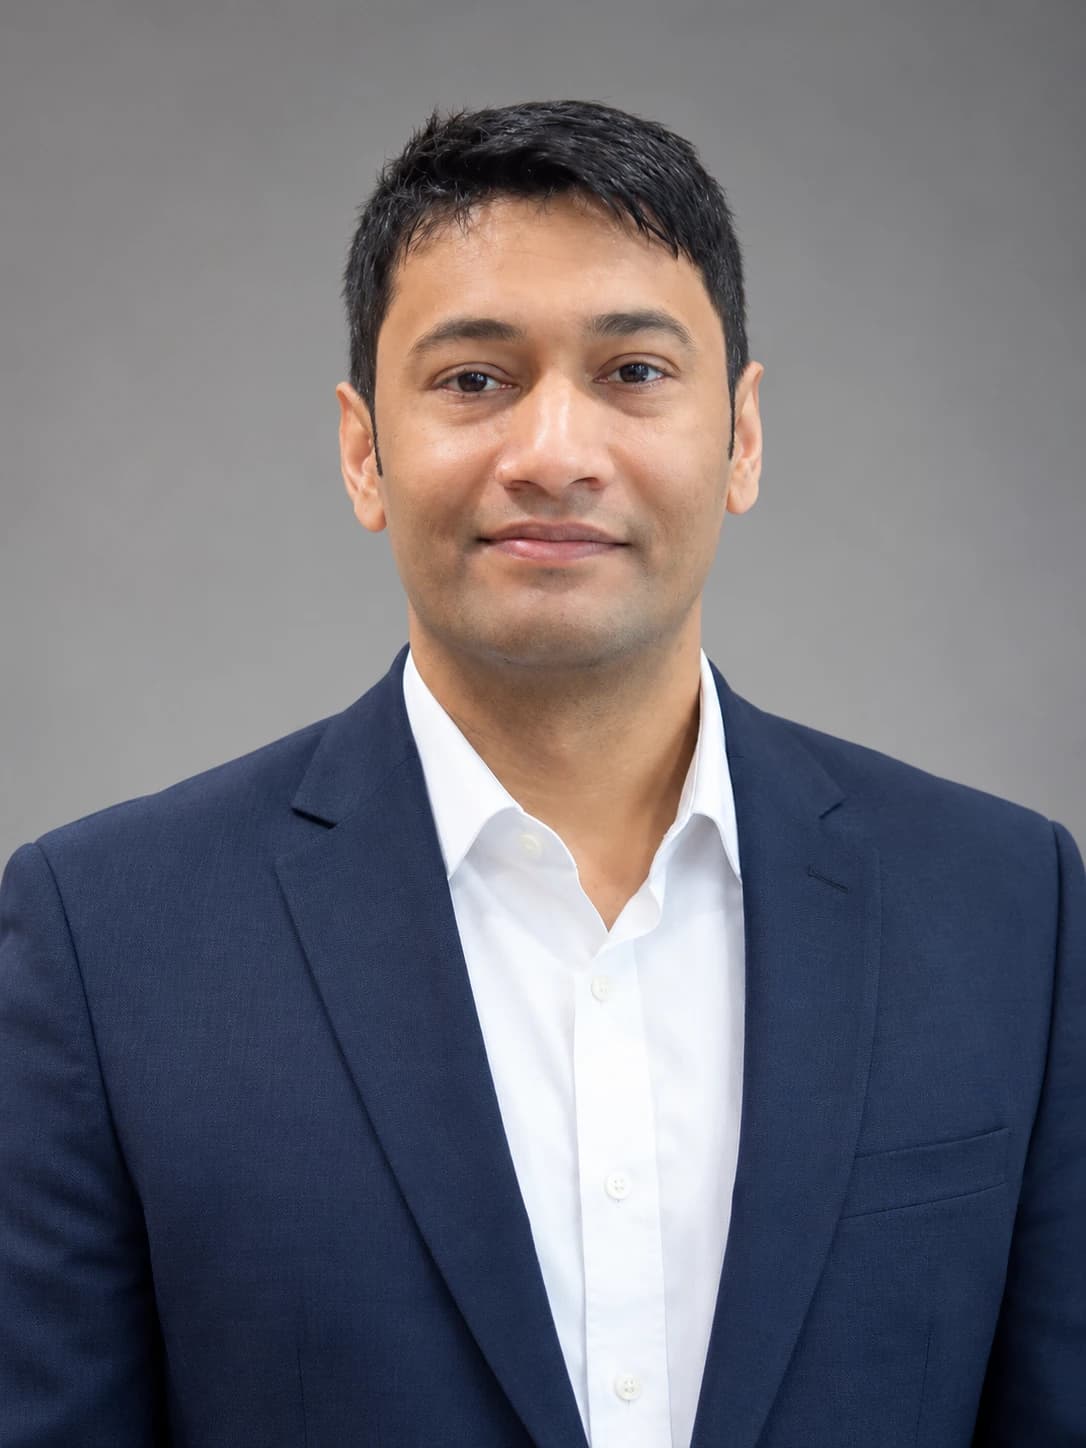
Co-Founder, Operations & Business Development
Yusuf Ali Khan
Yusuf holds an ISO 27001 Lead Auditor certification and a Master of Cybersecurity from Monash University. His background spans security operations, governance, risk and compliance, and security risk management, built over roles at Reliance Industries, Tata Steel and Infosys, working on converged physical and electronic security operations, monitoring and incident handling, and risk and compliance across large, multi-site enterprises.
That operations background is why VicByte engagements run the way they do. Clients and learners get more than expertise: they get a process with clear timelines, responsive communication, and nothing left to chase.
An ecosystem, not a one-off engagement
Most providers hand over a report and leave. We stay with you through the full cycle, from first assessment to a team that can carry the work forward.
Advise
ISO 27001 consulting
Gap assessments, ISMS implementation, and independent internal audits, taking you from an uncertain starting point to certification and beyond.
View services →Test
Penetration testing and AI red teaming
Adversarial testing that shows exactly what an attacker would find in your applications, infrastructure and AI systems, so your controls are proven, not assumed.
View testing services →Train
VicByte Academy: capability for your own teams
Internal auditor and AI red teaming training that builds skills inside your organisation, so you are not dependent on outside help to stay secure.
Explore VicByte Academy →How the pieces fit together
Each stage feeds the next, and the cycle repeats as your organisation grows.
- 1
Assess
Score where you stand against the standard, with evidence.
- 2
Implement
Build the ISMS and controls that close the gaps.
- 3
Test
Validate those controls against real attacker techniques.
- 4
Train
Equip your people to run, audit and defend it themselves.
How we work
The standards we hold ourselves to.
Fixed scope, fixed fee
No hourly billing and no scope creep. You know the cost before work begins.
Scored against evidence
Every requirement is rated CONFORMANT, PARTIAL or GAP, so results are defensible and measurable.
Senior-led ISO advisory
You work directly with the specialist leading your ISO 27001 engagement, from first call to final report. No handoffs, no rotating account teams.
Independent by design
We prepare you for audit. Certification decisions stay with independent accredited bodies, as they should.
Let’s build your security capability, not just your report.
Questions first? Read the FAQ